Compliance

Compliance Services

Regulators, insurers and clients expect proof that your data is protected. We identify gaps, fix vulnerabilities and deliver the documentation you need to demonstrate compliance.

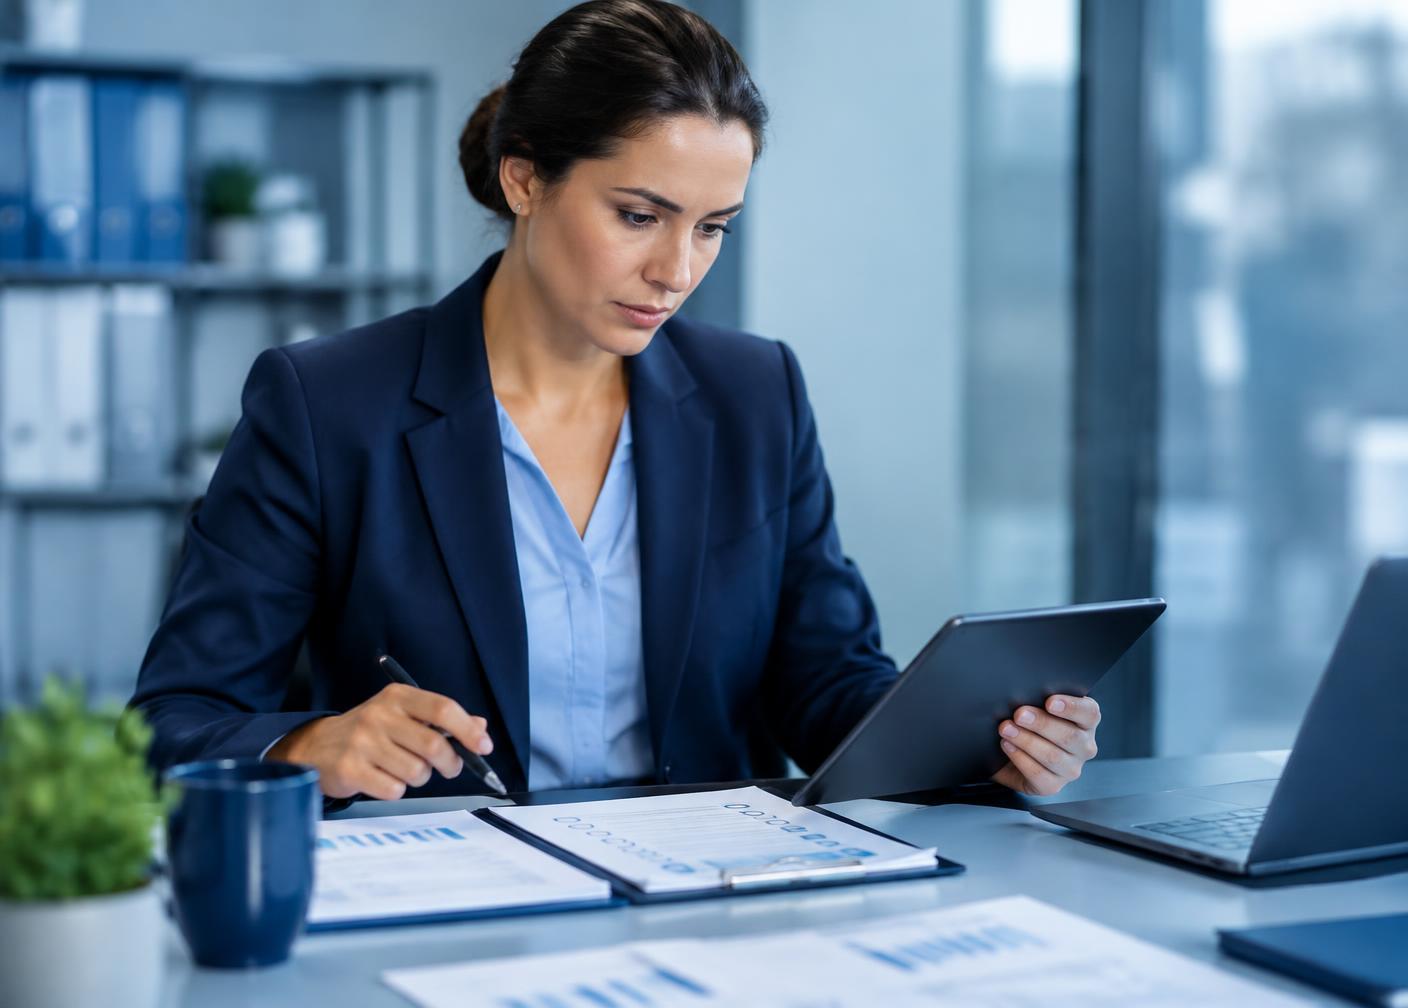
Compliance specialist reviewing a security risk assessment report

What you get

Assess, remediate and document — with confidence.

  • Clear view of your risk posture
  • Vulnerabilities fixed, not just found
  • Audit-ready documentation
  • Support for HIPAA and cyber-insurance requirements
01

Vulnerability Scanning / Reporting Services

Scheduled internal and external scans that uncover weaknesses across your network, with clear, prioritized reports.

  • Internal and external vulnerability scans
  • Risk-ranked findings with remediation guidance
  • Executive and technical reports
  • Trend tracking over time
02

Real-time Vulnerability Remediation Services

We don't just hand you a list — our engineers fix vulnerabilities as they're discovered to shrink your exposure window.

  • Continuous detection-to-fix workflow
  • Prioritization by severity and exploitability
  • Configuration hardening
  • Verification scans after remediation
03

HIPAA Security Risk Assessments

A thorough review of how your organization protects electronic protected health information (ePHI) under the HIPAA Security Rule.

  • Administrative, physical and technical safeguard review
  • Identification of threats to ePHI
  • Risk ratings and remediation plan
  • Documentation to support HIPAA requirements
04

Cybersecurity Risk Assessments

A business-focused evaluation of your security controls, mapped to recognized frameworks, with a practical roadmap.

  • Control assessment aligned to frameworks such as NIST CSF
  • Policy and process review
  • Prioritized, budget-aware roadmap
  • Support for cyber-insurance questionnaires
05

Penetration Testing

Controlled, ethical attacks that show how a real adversary could break in — before they do.

  • External and internal network testing
  • Web application testing
  • Social engineering assessments
  • Detailed findings with proof and fixes
06

Reporting and Documentation

Policies, procedures and evidence packages that keep you audit-ready and make compliance easy to demonstrate.

  • Security policy and procedure development
  • Audit evidence collection
  • Board and executive reporting
  • Ongoing documentation updates

Explore more

Ready for IT that just works?

Schedule an assessment. We'll review your environment and show you exactly where you stand.

Talk to an expert